5 Splunk checks before heading on holiday!

Summer is here, teams are easing off the gas – and this year, the World Cup makes slowing down even more tempting 🏆⚽. But while your colleagues take time off, your data never stops. That’s the whole paradox of the summer “IT freeze”: fewer people at the controls, while the platform keeps ingesting, indexing and […]

Splunk v10 Effective Configuration

The Effective Configuration Add-On saves time and eliminates the need to contact other teams if you’re not managing all Splunk elements, helping you access the information you need in seconds instead of days. Using the Effective Configuration Add-On also allows you to view the current effective configuration on selected agents and check parameter’s values set […]

Splunk v10 Remote Upgrader

Introduction Here is a quick review of the Remote Upgrader Feature provided with the brand new Splunk version 10, that was released in July. This new feature allows you to upgrade (or downgrade) your Agents distributed across your Splunk infrastructure managed by your Agent Management, formerly known as Deployment Server. Limitations There are not a […]

Splunk v10 Edge Processor

Introduction Splunk 10 was released on July 28, 2025. One of the main new feature is the Edge Processor. The Edge Processor solution is “a service hosted within your Splunk Enterprise deployment designed to help you manage data ingestion within your network boundaries. Use the Edge Processor solution to filter, mask, and transform your data […]

Splunk ES 8.0.2 – Response Plans & Investigation types

Table of contents Here is a second post about Splunk Enterprise Security 8.0.2, released on January 22nd. This time, I will give you an overview of the Response Plans feature. You can access to Responses Plans by going to Splunk Enterprise Security > Security Content > Response Plans. What Are Response Plans ? The Splunk […]

Splunk ES 8.0.2 – Versioning feature review

Table of contents Splunk Enterprise Security v8.0.2 is out since January, 22nd. I will present to you a new feature introduced in this version: detection versioning. Long awaited, this functionality is interesting in several ways. First of all, in theory, you can avoid using Git or GitLab to keep versions of your detections, as it […]

Octamis Recognized in 2022 Splunk Regional Partner Awards

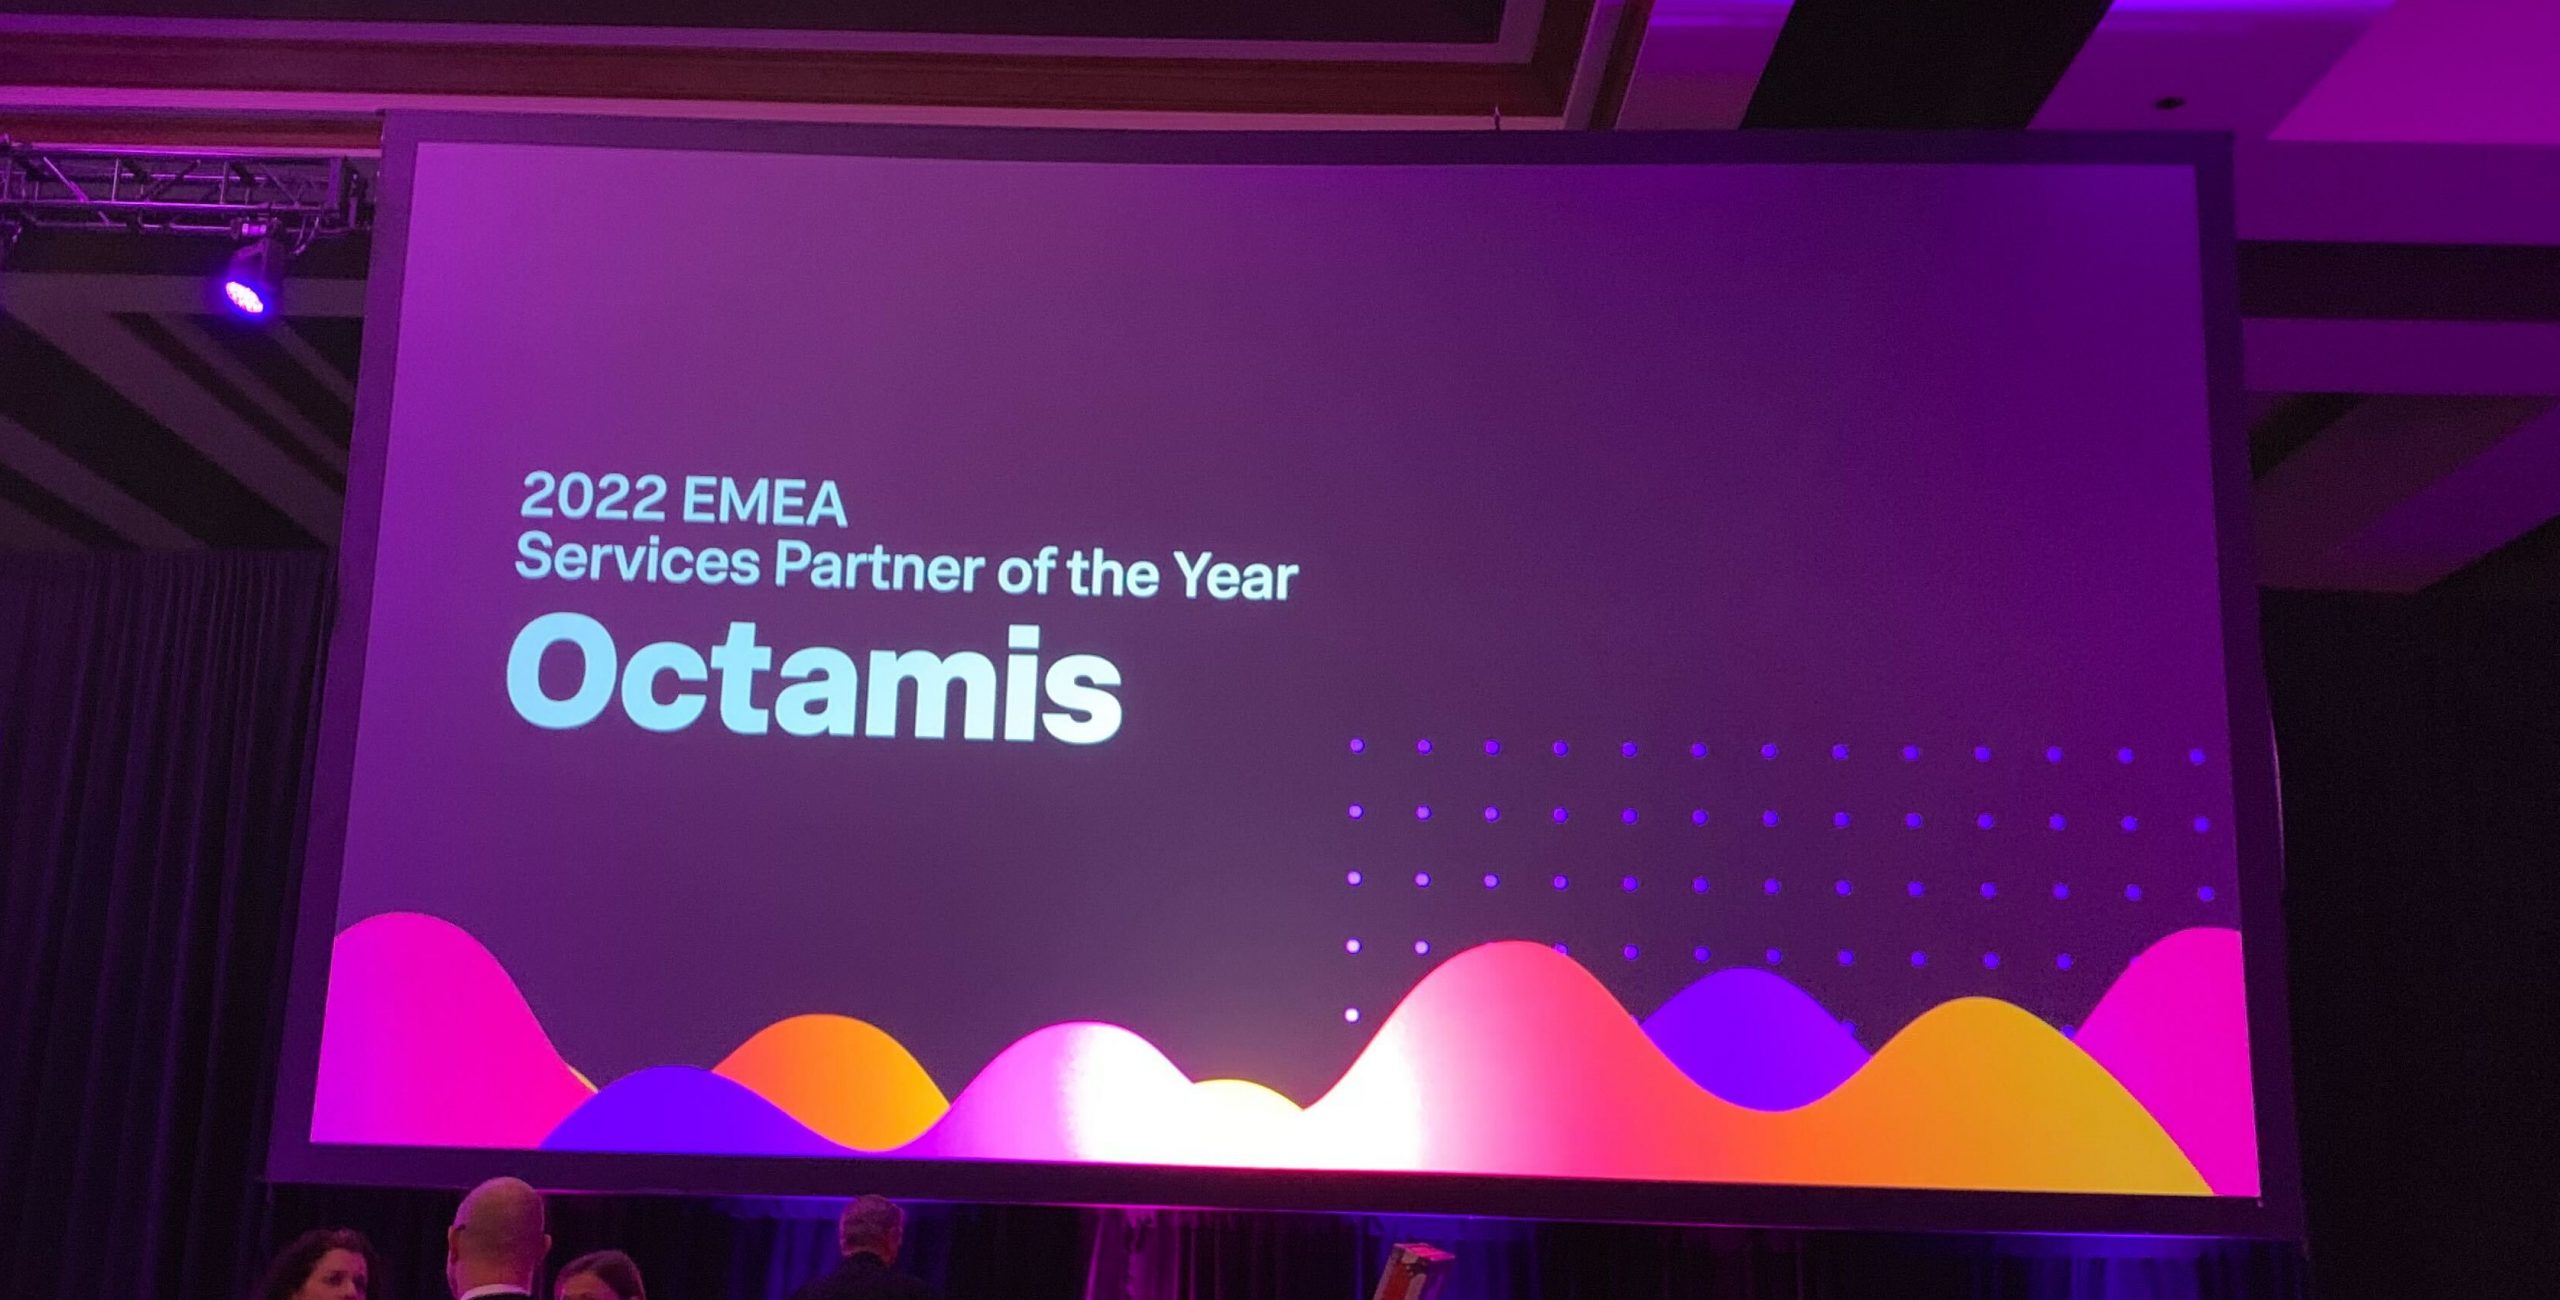
Octamis Named 2022 EMEA Professional Services Partner of the Year Winner for Outstanding Regional Performance LONDON – June 15, 2022 – Octamis today announced it has received the 2022 EMEA Professional Services Partner of the Year award for exceptional performance and commitment to Splunk’s Partnerverse. This regional award recognizes a partner  that is actively engaged […]

Octamis Recognized in 2020 Splunk Regional Partner Awards

Octamis Named 2020 EMEA Professional Services Partner of the Year Winner for Outstanding Regional Performance London – October 7th, 2020 – Octamis today announced it has received the 2020 EMEA Professional Services Partner of the Year award for exceptional performance and commitment to Splunk’s Partner+ Program. The 2020 EMEA Professional Services Partner of the Year award recognizes an EMEA […]

Nmon Performance for Splunk VERSUS Splunk app for unix and TA-unix

As a fellow Splunker since many years now, I had the chance to develop and maintain the Nmon Performance application for Splunk, with the goal to get the best features and user experience to provide a strong and complete monitoring solution for your Unix and Linux servers. In this article, I will compare (as much […]

Scroll to top